
Passware
The world leader in encrypted electronic evidence discovery and decryption.
Passware Kit Mobile
Forensic tool that extracts and decrypts user data from mobile devices.

State-of-the-art mobile forensic tool
Passware forensic products are used by the world’s top law enforcement agencies to crack cases where decryption is required – with a 70 percent success rate. Our team has worked hard to build the next generation of decryption solutions for mobile devices – Passware Kit Mobile.
Why let a locked phone stop you from solving a case? Passware Kit Mobile is an easy-to-use Android and iPhone forensics tool, which extracts and decrypts data, and supports iPhone data recovery from disabled devices.
Bypass or Recovery of Passcodes
Bypasses or recovers pattern, password, PIN, and alpha-numeric passcode locks. Extracts data from locked or encrypted mobile devices and smartwatches.
Low-level Access
Forensically-sound full file-system extraction. Works with devices protected by Mobile Device Management solutions, with OTG disabled, or stuck in a boot loop. Extracts encryption keys from hardware-backed Keystore.
Advanced Data Extraction
Extracts iOS Keychain data and passwords from 1Password, Enpass, and Dashlane managers. Creates a decrypted copy of Keychain for further analysis. Decrypts data from Second Space accounts, Signal and Wickr messengers. All using a single extraction credit.
Accelerated Recovery
Accelerates the recovery of unlock codes for supported devices with NVIDIA, AMD, and Intel Arc GPUs and distributed computing.
Decrypts Multiple Devices in Parallel
The multi-window mode enables simultaneous processing of mobile devices.
Regular Updates and Quick Support
One business-day customer support, case-by-case approach. Quarterly updates and new devices being added on a regular basis.
Licensing Options
Passware Kit Mobile is available for law enforcement and other types of government organizations and private companies with justifiable business needs, such as forensic firms or corporate investigation teams. We do not sell to individuals.
Passware Kit Mobile is available as an annual license with unlimited device extractions, or as a Starter edition, limited to 60 days and 5 successful extractions.
Supported Devices
Apple Devices
Android Devices
iPhone 7, 7 Plus, 6S, 6S Plus, SE, 6, 6 Plus, 5C, 5, 4S
iPad Air 2, iPad 7th Gen, iPad Pro
P Smart 2021, P30, P20 Pro, Honor 10, other MediaTek, Kirin, and Qualcomm
MediaTek, Qualcomm
MediaTek, Qualcomm
Exynos (incl. S21 series and Watch4/5/6), MediaTek, Qualcomm, Unisoc
Nokia, Lenovo, Alcatel, Blackview, Doogee, HTC, Motorola, Meizu, Oppo, OnePlus, Sony, Vivo, ZTE, etc.
For more information please contact MergenPro’s sales team on info@mergenpro.com
Passware Kit Forensic
The complete encrypted electronic evidence discovery solution.

The world leader in encrypted electronic evidence discovery and decryption
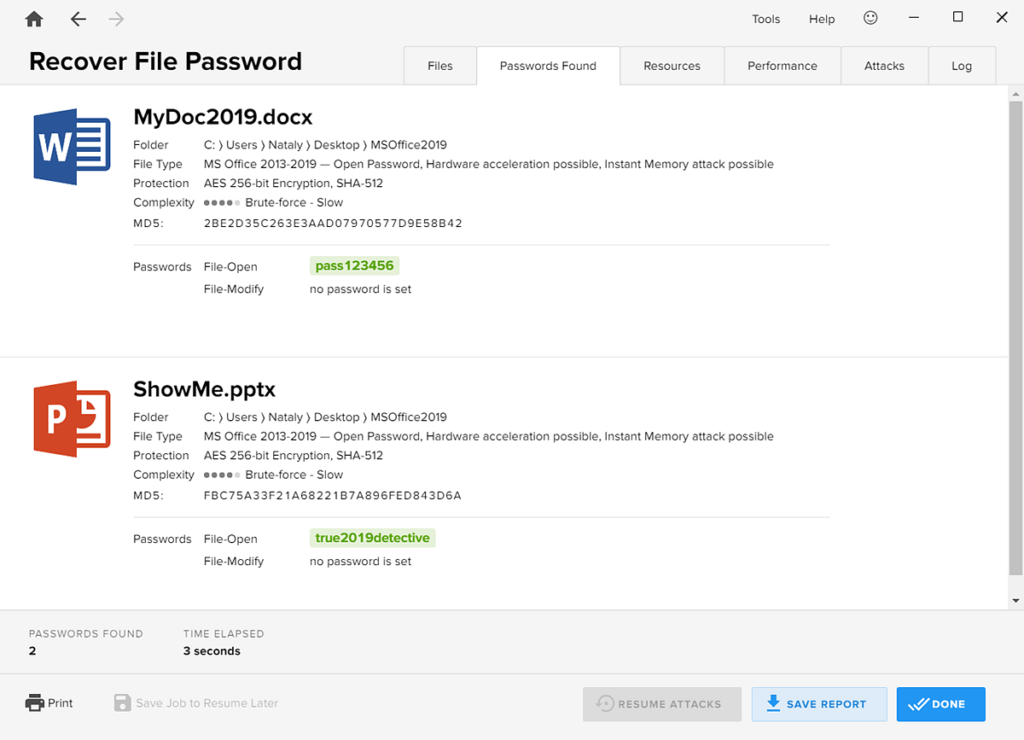
Passware Kit Forensic is the complete encrypted electronic evidence discovery solution that reports and decrypts all password-protected items on a computer. The software recognizes 300+ file types and works in batch mode recovering passwords.
Password recovery for over 420 file types
MS Office, PDF, Zip and RAR, QuickBooks, FileMaker, Lotus Notes, Bitcoin wallets, Apple iTunes Backup, Mac OS X Keychain, password managers, and many other popular applications.
Full disk decryption
Decrypts or recovers passwords for APFS, Apple DMG, BitLocker, Dell, eCryptfs, FileVault2, LUKS and LUKS2, McAfee, PGP, SanDisk, Steganos, Symantec, TrueCrypt, and VeraCrypt containers, disk images, folders, and vaults. Supports batch processing.
Optional Device Decryption Add-on unlocks, decrypts, and recovers passwords for: WD My Passport and My Book, Transcend, Seagate and LaCie disks, Lenovo ThinkPads, BitLocker-encrypted devices with TPM, and Macs with Apple T2 Security Chips, including ones protected with EFI firmware password. Available for law enforcement and other types of government organizations.

Live memory analysis
Analyzes live memory images and hibernation files and extracts encryption keys for hard disks and logins for Windows & Mac accounts. Passware Bootable Memory Imager acquires memory of Windows, Linux, and Mac computers.

The complete encrypted electronic evidence discovery solution
Password recovery for over 420 file types
MS Office, PDF, Zip and RAR, QuickBooks, FileMaker, Lotus Notes, Bitcoin wallets, Apple iTunes Backup, Mac OS X Keychain, password managers, and many other popular applications.
GPU acceleration & resource management
Accelerated password recovery with multiple computers, NVIDIA, AMD, and Intel Arc GPUs, and Rainbow Tables. Built-in Resource Manager makes it easy to set up and monitor a hardware cluster. Caches previously tested passwords to eliminate redundant checks and improve the overall password recovery performance.
Live memory analysis
Analyzes memory images and hibernation files and extracts encryption keys for hard disks and files and passwords for Windows/Mac accounts and websites. Acquires memory of Windows, Linux, and Mac computers.
Batch processing
Runs password recovery tasks for multiple files and FDE images without user interaction. Smart resource allocation algorithm for concurrent file processing minimizes hardware idle time. Fast transferring of the password recovery process to another computer using digests instead of large files or disk images. Automatic check of the recovered passwords for previous and skipped files in a session.
Mac version
In addition to all the key features of a Windows version, Passware Kit Forensic for Mac provides access to APFS disks from Mac computers with Apple T2 chip.
Intelligent detection
Detects all encrypted files and hard disk images and reports the type of encryption and the complexity of the decryption.
Automatic updates
Optional automatic software and agents updates with one year of Software Maintenance and Support (SMS) subscription.
Passware Kit Agents
Support for distributed password recovery for Windows, Linux, and Amazon EC2. The Linux version runs a portable Passware Kit Agent from a bootable Linux USB drive.
Decryption of FDE
Decrypts or recovers passwords for APFS, Apple DMG, BitLocker, Dell, eCryptfs, FileVault2, LUKS/LUKS2, McAfee, PGP, SanDisk, Steganos, Symantec, and TrueCrypt/VeraCrypt containers, disk images, folders, and vaults. Optional Device Decryption Add-on recovers passwords or recovery keys for: WD My Passport and My Book, Transcend, Seagate and LaCie disks, Lenovo ThinkPads, BitLocker-encrypted devices with TPM, and Macs with Apple T2 Security Chips.
Hardware acceleration of password recovery attacks
Accelerated password recovery with multiple computers, NVIDIA and AMD GPUs, and Rainbow Tables.

For more information please contact MergenPro’s sales team on info@mergenpro.com
Passware Kit Agent
Network Distributed Password Recovery
A network distributed password recovery worker for Passware Kit Ultimate, Forensic, Business, and Mobile editions.
Passware Kit Ultimate, Forensic, Business, and Mobile editions distribute password recovery tasks over a network of Windows or Linux computers, as well as Amazon EC2 and Microsoft Azure Cloud Agents, for linear scalability. Each computer running Passware Kit Agent can simultaneously support multiple CPUs and GPUs. The built-in Resource Manager allows forensic examiners to easily configure, manage, and monitor a hardware cluster. Passware Kit includes 5 Agents in the Forensic edition, 10 Agents in the Ultimate edition, and 2 Agents in the Mobile edition, with the ability to purchase more Agents individually as needed. All the Agents can be managed remotely directly from the Passware Kit.